
Headline 1 of 5
Latest news
 SecurityRefitter fixes code-execution flaw in version 2.1.2A GitHub security advisory says Refitter can enable arbitrary code execution in applications that compile clients generated from attacker-influenced OpenAPI descriptions. The advisory attributes the flaw to unescaped content-type values in generated code and says it verified the issue with Refitter 2.0.0 and .NET 8. Refitter versions earlier than 2.1.2 are affected; the advisory identifies 2.1.2 as patched and recommends upgrading and using trusted OpenAPI descriptions.
 SecurityJane advisory warns of code-generation risks in versions below 7.12.0A Jane security advisory published on November 20, 2026, warns that jane-php/open-api-3 versions below 7.12.0 can expose build and continuous-integration systems when generating PHP from attacker-influenced OpenAPI documents. During code generation, resolving external references can prompt requests to attacker-chosen URLs and read local files, with retrieved content potentially included in generated output. The advisory lists 7.12.0 as patched and recommends upgrading and restricting untrusted documents until patched.
 Securitydjango-docutils 0.30.0 blocks unsafe defaults that could expose filesThe django-docutils maintainers fixed unsafe Docutils defaults in version 0.30.0, affecting versions 0.29.0 and earlier when they render lower-trust reStructuredText (RST), a plain-text markup format. The GitHub advisory says the flaw arose because Docutils could process content without protective web-safe defaults, allowing it to access local files, make server-side requests, or emit raw HTML. Version 0.30.0 adds safer defaults and doctree sanitization; the advisory recommends upgrading and keeping unsafe settings disabled for lower-trust content.
 SecurityFlyto2 Core flaw allows file writes outside its sandboxAn advisory disclosed that an incomplete fix left an arbitrary-file-write vulnerability in Flyto2 Core, affecting versions through 2.26.7. The flaw let filesystem writes escape the configured sandbox because path validation was not applied centrally; 2.26.8 is listed as patched. The advisory says the flaw could enable code execution or full host compromise and recommends upgrading and reviewing filesystem-write protections.
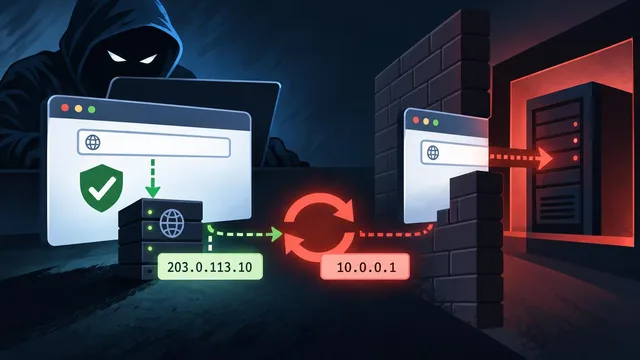 SecurityGitHub advisory flags SSRF risk in Flyto2 Core through 2.26.7GitHub published an advisory about a server-side request forgery risk in Flyto2 Core versions through 2.26.7. The advisory says differing address resolutions between hostname validation and the eventual connection could allow access to internal resources. The advisory lists 2.26.8 as patched; it gives no separate remediation instruction or publication date.
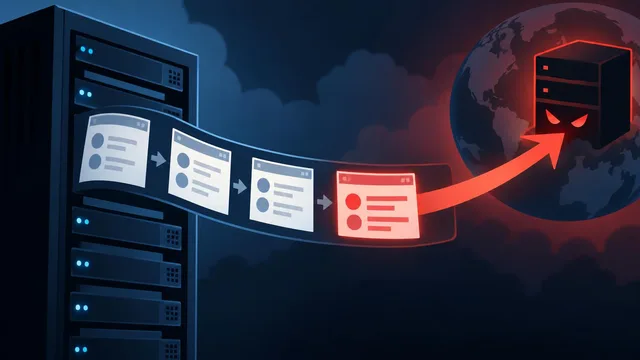 SecurityFlyto2 Core advisory flags SSRF flaw in pagination functionFlyto2 Core disclosed a server-side request forgery flaw in its pagination function, http.paginate, in an advisory published on 2026-11-20. The advisory says the function checked the initial URL but did not recheck server-supplied URLs used to fetch later pages, affecting pip package versions <= 2.26.7. The flaw could expose internal or metadata response content to the caller; the advisory lists 2.26.8 as patched.
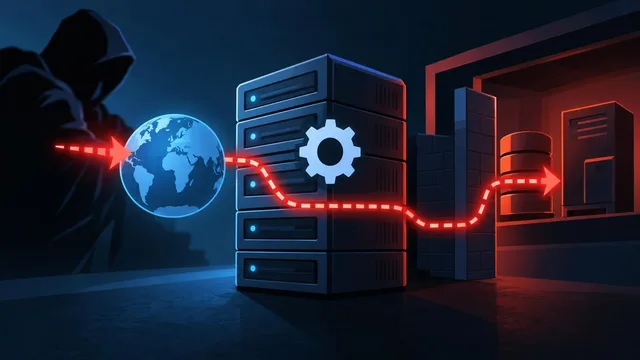 SecurityFlyto2 Core fixes SSRF guard bypass in version 2.26.8GitHub’s security advisory reports that Flyto2 Core’s server-side request forgery (SSRF) guard can be bypassed in versions 2.26.7 and earlier through DNS rebinding. The flaw arises because the guard checks an address but does not ensure the later connection uses that same address. The advisory identifies 2.26.8 as patched and recommends validating every resolved IP and connecting to a validated address.
 SecurityJupyter MCP Server flaw affects versions through 1.0.2GitHub published a security advisory for Jupyter MCP Server on 2026-11-20, identifying versions through 1.0.2 as affected. The advisory says unauthenticated management routes in standalone HTTP mode can permit unauthorized changes to server state and backend connection settings, weakening the intended authentication boundary. Users should update to 1.0.3, the patched version, and administrators should apply authentication consistently and restrict non-loopback listeners with an explicit host allowlist.
 SecurityJupyter MCP Server advisory flags flaw in versions through 1.0.2A security advisory identified a browser-origin vulnerability in Jupyter MCP Server versions through 1.0.2. The advisory says inconsistent Host and Origin validation could allow unauthorized changes to server state and traffic to attacker-controlled systems, a flaw fixed in 1.0.3. Administrators should update to 1.0.3 and limit network exposure, according to the advisory.
 SecurityDaptin fixes unauthenticated SQL injection in version 0.12.30Daptin maintainers disclosed an unauthenticated SQL injection flaw affecting versions 0.12.29 and earlier. The GitHub security advisory says insufficient validation of sort-column identifiers could disrupt database queries and expose data beyond a requester’s permissions. Administrators should upgrade affected installations to 0.12.30 or later, which the advisory lists as patched.
 SecurityDaptin fixes access-control flaw in YJS collaboration endpointDaptin maintainers disclosed and fixed an access-control flaw in the generic YJS collaboration endpoint, affecting versions 0.11.4 through versions before 0.12.30 when a deployment has at least one file-typed column. The endpoint checked for a user session but did not verify access to each resource, allowing authenticated users to read and edit collaborative content beyond their permissions. The fix applies existing read and update permissions to canonical database-backed rooms, but the advisory says no Daptin release containing the fix is listed yet.
 SecurityBolt patches open redirect vulnerability in LoginFormAuthenticatorBolt disclosed and patched an open redirect vulnerability in LoginFormAuthenticator, with the fix in version 6.1.4. The flaw affected the composerbolt/core package for Composer in versions earlier than 6.1.4 and could send users to attacker-controlled domains after login success or failure. The advisory says the redirects could enable phishing and potential token theft; administrators should update to version 6.1.4.
 SecurityBolt discloses SSRF flaw in composerbolt/core, patched in 6.1.4Bolt disclosed a server-side request forgery vulnerability in two authenticated backend endpoints in the composerbolt/core package, affecting versions earlier than 6.1.4. The endpoints fetched user-supplied URLs from the server without protections against requests to internal targets. Bolt patched the issue in 6.1.4; users of earlier versions should update to that version or later.
 SecurityBolt fixes unauthenticated content-metadata exposure in version 6.1.4Bolt disclosed an information-disclosure vulnerability in its public Relation API affecting composerbolt/core versions earlier than 6.1.4. The missing access-control filter allowed unauthenticated users to discover metadata about unpublished, draft and viewless content through REST and GraphQL endpoints. Bolt patched the flaw in version 6.1.4; administrators should upgrade to that version.
 SecurityBolt patches SSRF flaw in version 6.1.5Bolt patched a flaw that could trick its server into sending requests to unintended destinations, a vulnerability known as server-side request forgery, in version 6.1.5. The advisory says authenticated users could exploit unchecked redirects in composerbolt/core versions earlier than 6.1.5 to direct server requests to internal or cloud-metadata addresses. The issue is fixed in Bolt 6.1.5; administrators should upgrade affected installations to that version.
 SecurityBolt fixes SQL injection flaw in version 6.1.4Bolt patched a SQL injection vulnerability in ListFormatHelper with 6.1.4. The GitHub advisory says the flaw affected composerbolt/core versions < 6.1.4 and could expose database contents under specific conditions. Administrators should upgrade to Bolt 6.1.4 or later; the reported risk applies when general/caching/list_format is enabled.
 Securityfalcon-rust sampler flaw affects releases through 0.1.3A security advisory says falcon-rust has an insufficiently precise sampler in versions through 0.1.3, with version 0.2.0 identified as patched. The advisory reports a maximum relative error of 2^-33, above the roughly 2^-40 to 2^-46 range cited in security analyses, and says Falcon’s known-answer test vectors no longer match. The flaw affects the distributions used for signatures and key generation, but the advisory does not report a demonstrated end-to-end key recovery; users of affected releases should upgrade to 0.2.0.
 SecuritybaserCMS path-validation bypass leaves 5.2.3 vulnerable to remote code executionThe baserCMS security advisory reports that a flaw in the patch for CVE-2026-30940 leaves the content management system vulnerable to path traversal. The advisory says validation in BcThemeFileService can be skipped when a directory check using realpath() fails, and confirms the flaw was exploitable in 5.2.3. Versions earlier than 5.3.0 are listed as affected; administrators should upgrade to 5.3.0, the listed patched version.