
Flyto2 Core SSRF guard vulnerable to DNS-rebinding race
- Flyto2 Core
- SSRF
- DNS-rebinding
- TOCTOU
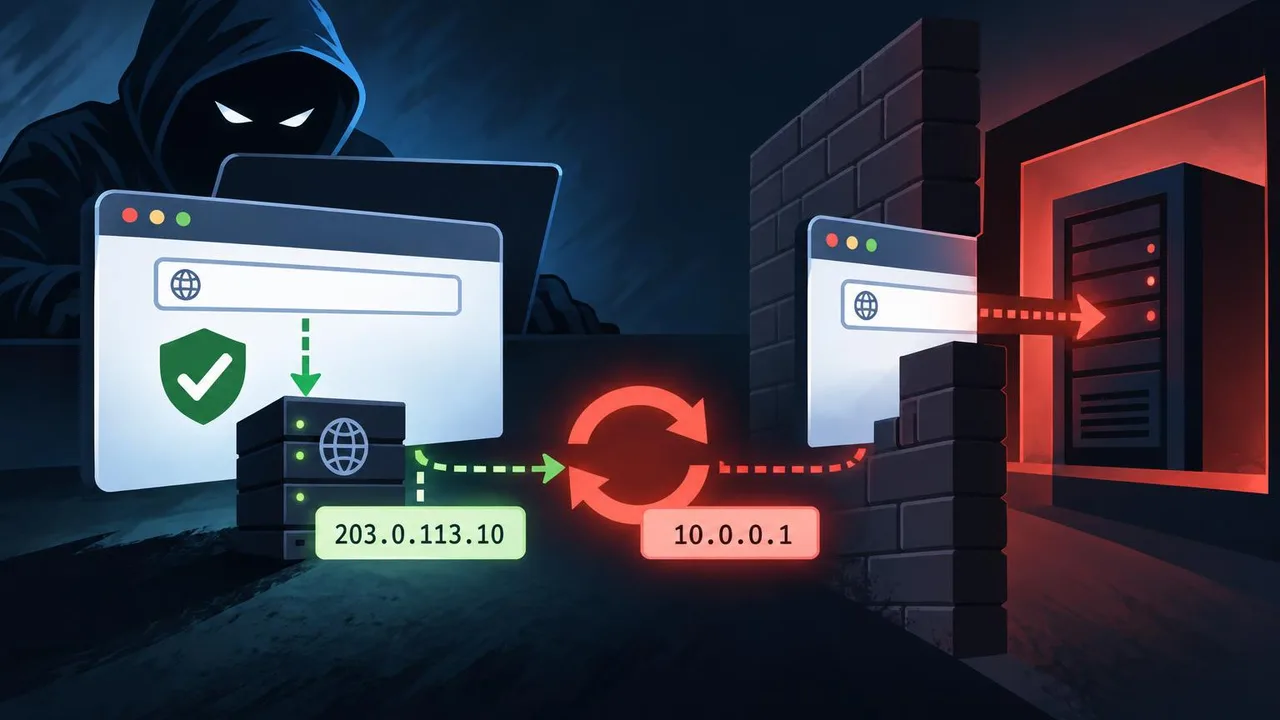
Flaw in validate_url_ssrf function enabled DNS-rebinding
Race condition allowed unauthorized internal network access
Version
2.26.8is listed as the patched release
A security advisory reports that Flyto2 Core’s `validate_url_ssrf` function has a server-side request forgery (SSRF) flaw affecting versions up to and including 2.26.7. The listed patched version is 2.26.8.
The function checks a hostname’s resolved IP address against private network ranges, but then returns the hostname instead of the checked address. The `aiohttp` library resolves the hostname again when it connects, creating a time-of-check to time-of-use (TOCTOU) race that can bypass the check.
The advisory says the flaw affects all modules that use `validate_url_ssrf` for internal fetches. It also says the documentation file `SECURITY_SSRF.md` incorrectly claims that the guard prevents DNS rebinding.
Key terms explained
- SSRF
SSRF is a vulnerability where an attacker manipulates a server into making unauthorized requests to internal or external resources. It allows attackers to interact with services that are otherwise inaccessible from the public internet.
Think of it this way. It is like tricking a security guard at the front desk into letting a stranger into a restricted area by showing them a fake delivery order.



