Inscriptis reports quadratic memory-growth vulnerability in get_text()
- Inscriptis
- HTML
- memory exhaustion
Sibling tables can make output grow with the square of their number
A 240 KB HTML document can generate about 1 billion characters
Converting untrusted HTML can exhaust application memory
Inscriptis reported a vulnerability in its `get_text()` function in an advisory published on November 20, 2026. Applications that use the function to convert untrusted HTML may run out of memory.
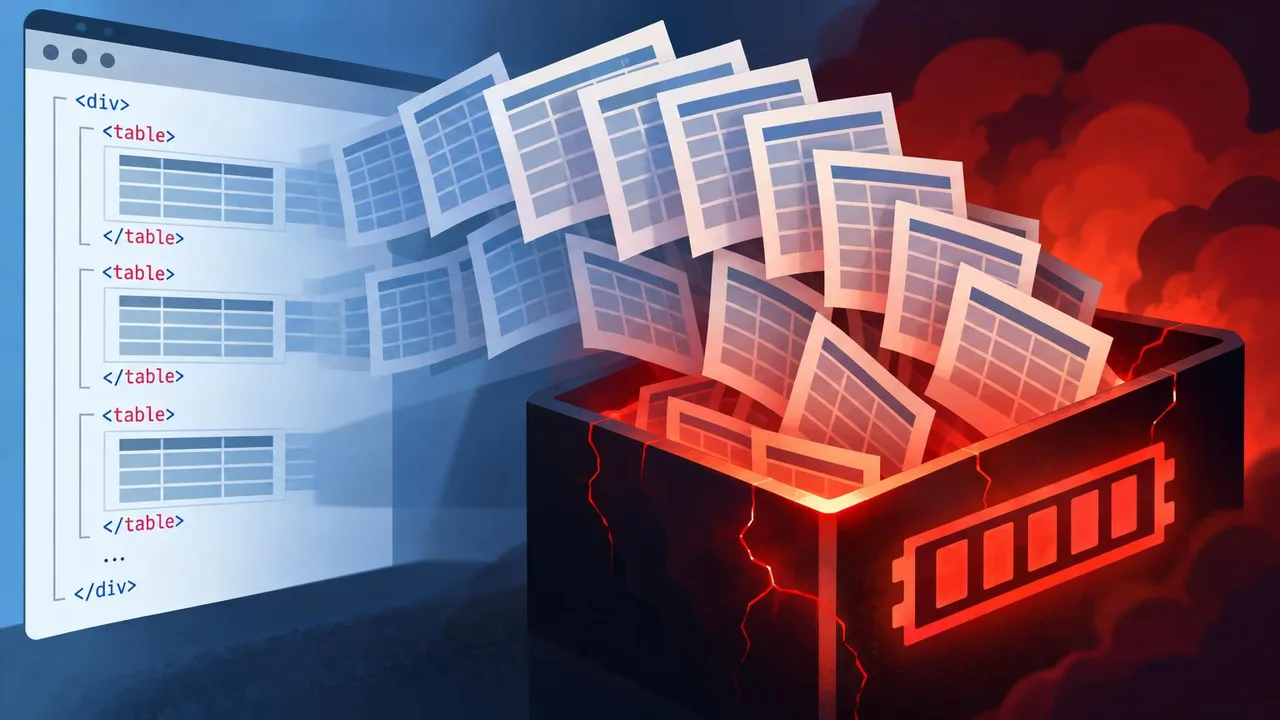
The issue arises when HTML contains sibling `<table>` elements. Each table adds another level of indentation to the parent, causing the generated text to grow quadratically as the number of tables increases.
In the advisory’s example, a 240 KB HTML document can generate approximately 1 billion characters of output and consume about 1 GB of memory. The impact applies to applications converting untrusted HTML; the advisory provides no release-state information.