
Headline 1 of 5
Latest news
 SecurityVMware vCenter flaw lets network attackers bypass authenticationBroadcom VMware vCenter has an authentication-bypass flaw in its VMware Directory Service that can let an attacker with network access gain unauthorized system access. The flaw can be exploited without authentication, and CISA advises administrators to assess each asset’s internet exposure and follow vendor mitigation instructions. The supplied advisory identifies no affected versions or specific patch; it says to follow applicable cloud-service guidance under BOD 26-04 or discontinue use if mitigations are unavailable.
 SecurityCISA lists Cisco Expressway vulnerability with conditional root-level impactCISA added a hard-coded credentials vulnerability in the Cisco Expressway Series to its Known Exploited Vulnerabilities Catalog on November 20, 2026. CISA says the flaw can permit remote command execution with root privileges on a clustered device, subject to access and other conditions. CISA advises applying vendor mitigations and applicable BOD 26-04 guidance, or discontinuing use if mitigations are unavailable.
 SecurityPaymenter advisory flags unauthenticated flaw in Livewire componentsPaymenter’s security advisory reports that a flaw in client-facing Livewire components could let unauthenticated attackers invoke public methods. The advisory lists versions through 1.5.6 as affected and 1.5.7 as patched. The potential impact depends on each component’s exposed methods and properties; administrators should upgrade and verify their deployed version.
 SecurityOHTTP codecs can retain memory on idle connectionsThe GitHub advisory reports that OHTTP client and server codecs retain a consumed buffer after a valid exchange, affecting versions 0.0.20.Final–0.0.26.Final. The codecs keep the encrypted outer content buffer until later inbound content replaces it or the handler or channel is removed, and 0.0.27.Final contains the fix. The retained buffer can pin memory on idle keep-alive connections and create availability pressure across many long-lived connections, but the advisory says it does not grow without bound per exchange on a single connection.
 SecurityGitHub lists affected CKAN versions in session-fixation advisoryGitHub published advisory GHSA-6499-jgj4-2wpf for a medium-severity session-fixation vulnerability in CKAN. The advisory lists CKAN versions earlier than 2.10.11 and versions 2.11.0 through 2.11.5 as affected. Administrators should check their CKAN installations and upgrade to a listed fixed version: 2.10.11 or 2.11.6.
 SecurityAdvisory says cargouu_split flaw can truncate a swapped fileA GitHub security advisory says a flaw in the Rust package cargouu_split can allow a swapped file to be truncated. The advisory lists versions 0.9.0 and earlier as affected and identifies 0.10.0 as patched. Users of affected versions should update to 0.10.0 and verify which version is installed.
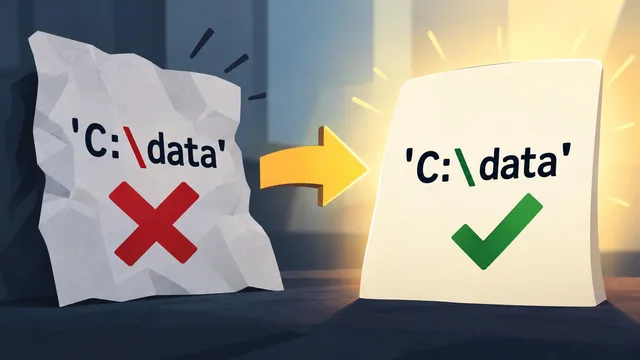 Securityuu_env rejects backslashes accepted by GNU envA GitHub security advisory reports that uu_env rejects backslashes in single-quoted strings that GNU env accepts. The advisory lists uu_env versions through 0.9.0 as affected and identifies 0.10.0 as patched. The confirmed scope is a difference in how the two tools handle backslashes in single-quoted strings; users can check their uu_env version against the advisory’s affected and patched versions.
 SecurityAdvisory reports TOCTOU flaw in cargouu_chcon recursive relabelingA GitHub advisory reports a time-of-check-to-time-of-use (TOCTOU) flaw in cargouu_chcon’s recursive relabeling. The advisory says the operation is not anchored to the traversal directory file descriptor, leaving a gap between checking a filesystem object and using it. Versions through 0.9.0 are affected, and 0.10.0 is listed as patched; the advisory does not specify practical impact or affected audiences.
 SecurityGit LFS advises users to upgrade after SSH command-handling flawThe Git LFS project published an advisory on Nov. 20, 2026, warning that certain SSH configurations could expose remote hosts to command execution and recommending an upgrade to 3.8.1. The advisory says Git LFS versions 0.5.0 through 2.13.3 and v3 versions earlier than 3.8.1 are affected because SSH command arguments may not be safely separated. The project says 3.8.1 fixes the command-handling flaw and an HTTPS URL-encoding issue; the workaround limits SSH object transfers but does not stop authentication requests.
 SecurityGitHub advisory lists Git LFS versions affected by high-severity flawGitHub published a high-severity Git LFS advisory, CVE-2026-69261, on November 20, 2026. The advisory lists Git LFS versions 0.5.0 through 2.13.3 and v3 versions before 3.8.1 as affected; 3.8.1 is listed as patched for the v3 package line. The advisory does not state the issue’s general impact or recommend a remedy beyond listing the patched v3 version.
 SecurityFabio advisory says unnormalized route selection can bypass access controlsA security advisory for Fabio says its route selection can leave protected backend resources without configured access controls. The advisory says the flaw affects versions < 1.7.3 because access checks depend on route selection that uses an unnormalized request path. Fabio 1.7.3 is listed as patched, and administrators should upgrade to that version or later.
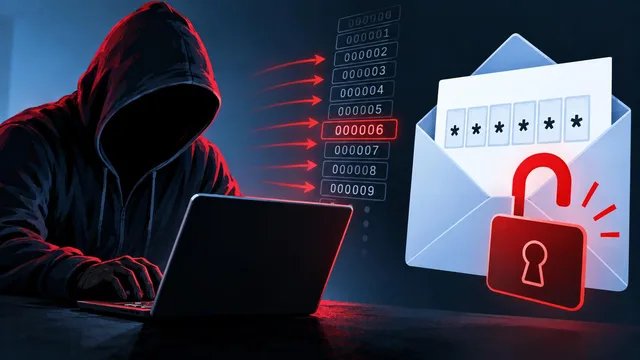 SecurityPoweradmin advisory reports email MFA bypass flawA security advisory reported a flaw in Poweradmin’s email-based multifactor authentication affecting versions 4.0.0 to before 4.2.6, 4.3.0 to before 4.3.5, and 4.4.0 to before 4.4.1. The advisory says the six-digit code used mt_rand() and had no failed-attempt limit, while codes remained valid for ten minutes and multifactor authentication was off by default. The affected release lines are fixed in 4.2.6, 4.3.5 and 4.4.1; users should upgrade to a patched version.
 SecurityGitHub advisory lists affected amqtt versionsGitHub published an advisory for the Python package amqtt, listing versions 0.11.0 through 0.12.0 as affected. The advisory lists 0.12.1 as the patched version. Users of amqtt should check their installations and update to version 0.12.1 or later.
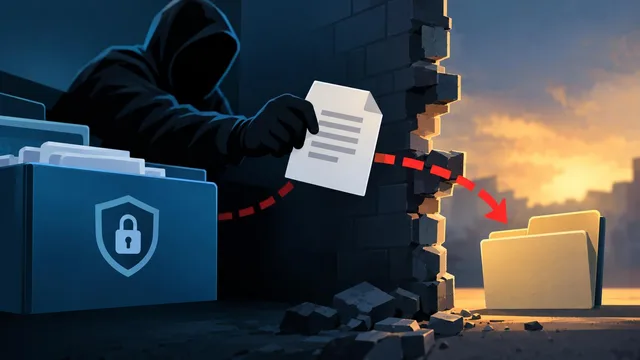 SecurityGitHub advises storyblok-backup users to upgradeGitHub published an advisory for a path traversal flaw in the npm package storyblok-backup, affecting versions through 0.7.0. The advisory says backup files could be written outside the intended directory and potentially overwrite files, depending on the backup process’s permissions. GitHub lists 0.7.1 as the patched version and recommends upgrading.
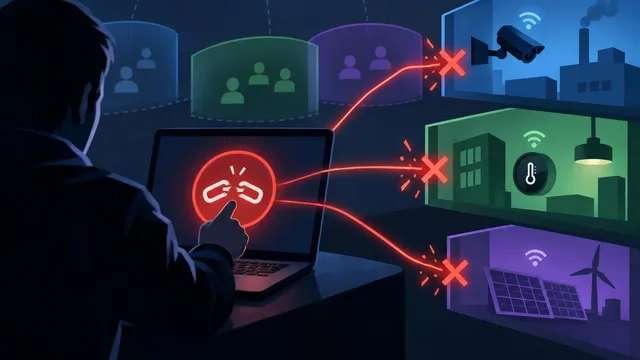 SecurityOpenRemote flaw could let users disconnect other tenants’ MQTT sessionsAn OpenRemote advisory says an authenticated user in one realm could disconnect MQTT sessions in other realms, crossing tenant boundaries through an authorization flaw in mavenio.openremote:openremote-manager. The GitHub advisory lists versions earlier than 1.31.0 as affected and says the flaw can disrupt device connectivity across tenants. Administrators should check multi-tenant deployments and upgrade to 1.31.0, the version listed as patched.
 SecurityGitHub warns of command-execution flaw in Git LFSGitHub published a security advisory on Nov. 20, 2026, warning that Git LFS can execute commands when it misparses crafted Git configuration for a submodule. The advisory lists affected releases as 0.6.0 through 2.13.3 and, in the v3 package line, versions 3.0.0 to before 3.8.1. GitHub says v3.8.1 fixes the issue and recommends upgrading; users who cannot upgrade should prevent submodule initialization and deactivate any already initialized submodules.
 SecurityGit LFS advisory lists affected releasesThe advisory identifies Git LFS releases in two package lines as affected. It was published on November 20, 2026, and rates the issue high severity. The database lists Git LFS v3.8.1 as a patched release.
 SecurityAppium storage plugin advisory flags file-deletion flaw in versions before 1.1.6GitHub Advisories reported on Nov. 20, 2026, that the Appium storage plugin allowed unauthenticated clients to delete files accessible to the Appium process. The advisory says versions earlier than 1.1.6 lacked validation to keep deletion within the intended storage area. Administrators should upgrade to version 1.1.6, restrict network access to Appium services and limit their permissions.