
OpenRemote flaw let authenticated users disconnect MQTT sessions across realms
- OpenRemote
- MQTT sessions
- multi-tenant IoT
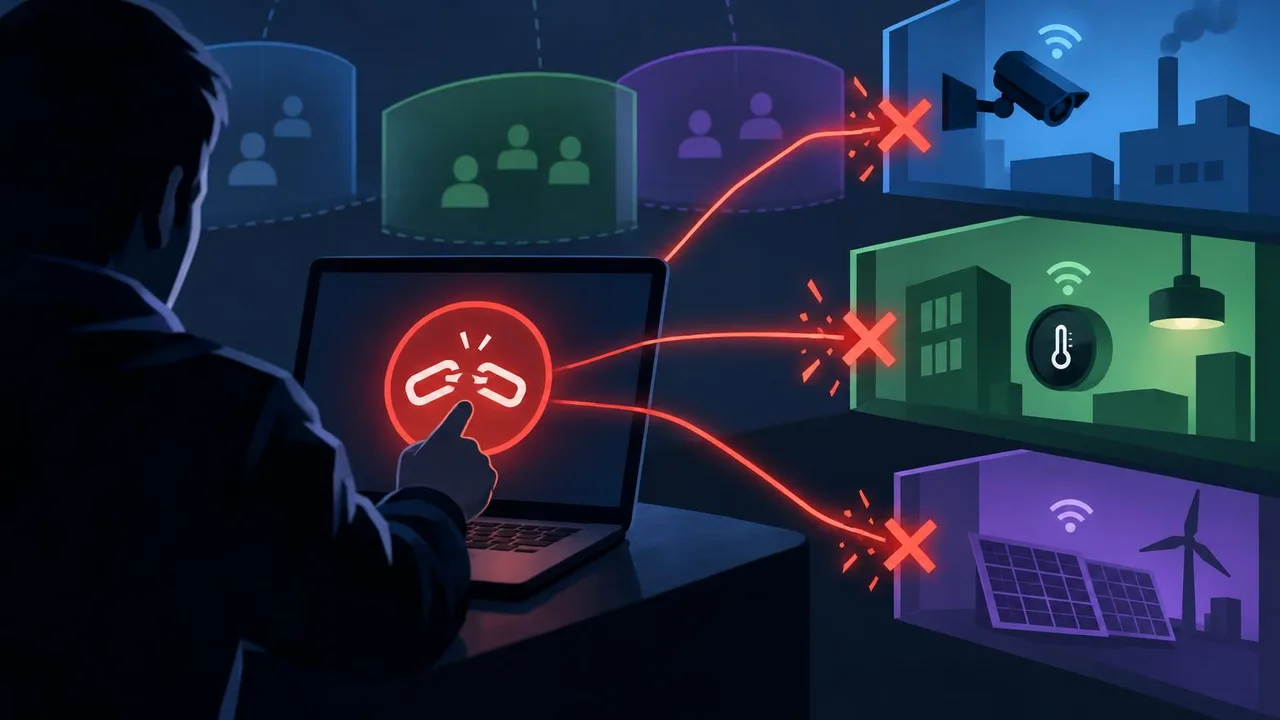
Versions before 1.31.0 were affected
The flaw could take IoT devices offline across tenant boundaries
OpenRemote fixed the issue in version 1.31.0
OpenRemote disclosed a vulnerability that allows an authenticated user in one realm to disconnect MQTT sessions in other realms without authorization. The disclosure was published on November 20, 2026.
The flaw affects OpenRemote versions before 1.31.0 in multi-tenant IoT deployments. MQTT is a messaging protocol used by devices to communicate; disconnecting its sessions can take sensors and actuators offline across tenant boundaries.
The issue can be exploited through HTTP GET requests, which makes it susceptible to cross-site request forgery (CSRF), a type of attack that tricks a user’s browser into sending an unwanted request. OpenRemote patched the vulnerability in version 1.31.0.



