
Headline 1 of 5
Latest news
 SecurityNLTK fixes parser flaw that can stop affected request workersNLTK published an advisory on a denial-of-service flaw in its semantic-logic type parser affecting versions <= 3.10.3. The advisory says parsing an untrusted type string or checking an expression against an attacker-influenced signature can trigger an unhandled RecursionError and stop the affected operation or request worker. NLTK 3.10.4 fixes the flaw; the advisory says it causes no memory corruption or code execution and does not affect confidentiality or integrity.
 SecurityNLTK warns of denial-of-service flaw in DependencyGraphNLTK maintainers issued an advisory about uncontrolled recursion in DependencyGraph, which can cause denial of service when applications process untrusted dependency data. The advisory lists NLTK versions <= 3.10.3 as affected and identifies 3.10.4 as patched. The flaw can terminate an affected operation or request worker; the advisory says it does not affect confidentiality or integrity and does not cause memory corruption or code execution.
 SecurityNLTK fixes CCG parser flaw that can terminate affected requestsGitHub published an advisory on November 19, 2026, warning that NLTK applications parsing untrusted CCG lexicon strings can encounter a denial-of-service flaw. The advisory says uncontrolled recursion can raise a RecursionError in 3.10.3 and earlier, affecting the lexicon-parsing operation. Administrators should upgrade to 3.10.4 and ensure applications handle parse errors when processing untrusted lexicon strings.
 SecurityNLTK advisory: custom WordNet resources can crash affected appsA security advisory reports uncontrolled recursion in Natural Language Toolkit’s Synset.tree() and Synset.acyclic_tree() methods. The advisory identifies NLTK versions through 3.10.3 as affected and says the traversal lacks a maximum-depth safeguard. Applications using custom WordNet-format resources can crash; the advisory lists 3.10.4 as the patched version.
 SecurityNLTK advisory: versions through 3.10.3 can crash on dependency dataA GitHub security advisory says Natural Language Toolkit versions through 3.10.3 contain a flaw that can crash processes handling certain dependency-parse data. The advisory reports that DependencyGraph.tree() and DependencyGraph.triples() use unbounded recursion, which can end in an unhandled RecursionError. The flaw may affect downstream applications processing user-supplied dependency data; the advisory identifies 3.10.4 as patched and recommends upgrading to that version or later.
 SecurityNLTK discloses ARFF_Formatter flaw affecting versions 3.10.3 and earlierNLTK maintainers disclosed an ARFF schema-injection vulnerability in ARFF_Formatter on November 19, 2026. The flaw stems from class labels being written into Weka ARFF declarations without quoting or escaping; versions 3.10.3 and earlier are affected. Applications using attacker-influenced training data may generate malformed ARFF files, and NLTK lists 3.10.4 as patched.
 SecurityNLTK fixes downloader flaw that can exhaust CPU and memoryNLTK maintainers disclosed a downloader denial-of-service flaw affecting versions from 3.6.7 to before 3.10.4. The advisory says cyclic collection references can cause an infinite walk classified as CWE-835. The advisory identifies 3.10.4 as the patched version and recommends updating.
 SecurityNLTK fixes XML corpus flaw that can drive CPU use quadraticallyNLTK’s security advisory reports a quadratic CPU denial-of-service flaw in XMLCorpusView. The advisory says the flaw affects NLTK versions 3.6 through 3.10.3 and is fixed in version 3.10.4. The reported risk applies to users processing affected, well-formed XML corpus files with a large comment or CDATA section; the advisory recommends upgrading to NLTK 3.10.4.
 SecurityReport finds additional sandbox bypass in NLTK 3.10.3An unidentified reporter disclosed an additional sandbox-bypass path in NLTK 3.10.3, saying the version’s earlier security fix was incomplete. The report says a Java-launch command-argument channel could bypass safeguards against running untrusted Java code; NLTK 3.10.4 is listed as patched. Successful exploitation could run attacker-selected Java bytecode with the privileges of the process using NLTK; administrators should upgrade and prevent untrusted inputs from controlling Java-launch settings.
 SecurityNLTK fixes corpus-reader flaw that could expose files across data rootsNLTK reported a security flaw in corpus-reader view methods that can expose files outside a corpus’s scoped boundary. The methods do not apply the corpus-root check used by CorpusReader.open(), allowing certain symlink paths to bypass that protection. The issue affects NLTK versions 3.9.4 and earlier versions below 3.10.4; upgrading to 3.10.4 is the stated fix, while exposure remains limited to files inside NLTK’s global data sandbox.
 SecurityNLTK 3.10.4 fixes file-access flaw in model loaderNLTK maintainers disclosed a security flaw in NLTK’s allowlisting unpickler affecting versions 3.10.0 through releases earlier than 3.10.4. The protection’s denylist missed some file-I/O functions in NumPy submodules when the unpickler allowed NumPy, SciPy and scikit-learn components. The flaw could allow file reads or file creation on a host loading an untrusted model, but the advisory says it does not enable code execution; 3.10.4 contains the fix.
 SecurityGitHub advises NLTK users to upgradeGitHub published a high-severity NLTK advisory, GHSA-wr3g-j6qj-xpgh. The advisory lists NLTK versions 3.9.4 through 3.10.3 as affected and 3.10.4 as patched. NLTK users should check their installations and upgrade to version 3.10.4 or later.
 Securitysnark-verifier maintainers disclose Halo 2 aggregation flawThe snark-verifier maintainers disclosed a flaw in the Halo 2 aggregation circuit that could mishandle proof elements encoded as the point at infinity. The advisory lists Rust package versions earlier than 0.2.5 as affected and 0.2.6 as patched; the circuit’s handling of identity points did not match an assumption in its elliptic-curve sum operation. The issue is rated medium severity, with practical exploitability dependent on surrounding aggregation and final-decider checks; administrators should update to version 0.2.6 or later and review those checks.
 SecurityNATS Server fixes MQTT bypass of subscription deny rulesNATS Server maintainers disclosed that MQTT retained messages and QoS replay can bypass subscription deny rules in affected versions of NATS Server. The advisory says the flaw affects versions below 2.12.12 and versions from 2.14.0-RC.1 to below 2.14.3. Administrators of affected deployments that use MQTT should upgrade to 2.12.12 or 2.14.3; deployments that do not use MQTT are not affected.
 SecurityNATS Server advisory flags availability risk for MQTT deploymentsGitHub’s advisory identifies a memory-exhaustion vulnerability in NATS Server versions 2.12.11 and below and 2.14.2. The advisory says unauthenticated users may cause memory exhaustion, while deployments not using MQTT are not affected. Deployments using MQTT should upgrade to 2.12.12 or 2.14.3.
 SecurityNATS Server flaw can crash JetStream in WebSocket-only setupsNATS Server’s security advisory warns that a vulnerability can crash JetStream servers in a WebSocket-only configuration before MQTT is enabled. The advisory lists NATS Server versions earlier than 2.12.12 and versions from 2.14.0-RC.1 up to, but not including, 2.14.3 as affected. Operators should upgrade affected 2.12-series deployments to 2.12.12 or affected 2.14-series deployments to 2.14.3; deployments without WebSocket, or using both WebSocket and MQTT, are not affected.
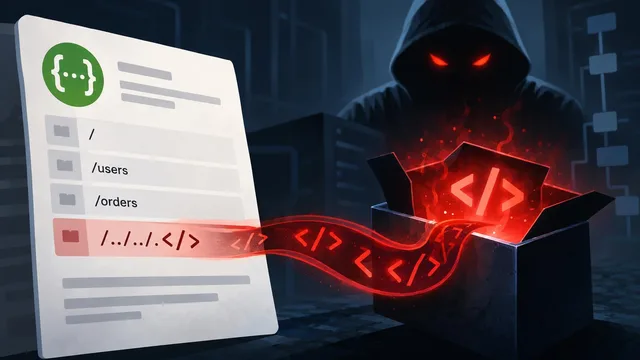 SecurityRefitter discloses code-execution flaw in versions before 2.1.2Refitter maintainers disclosed arbitrary code execution affecting Refitter versions earlier than 2.1.2 when generating clients from attacker-controlled or attacker-influenced OpenAPI descriptions. The advisory says Refitter inserts OpenAPI path values into generated code without safely handling them, allowing injected code to run when the generated assembly loads; the flaw was verified on Refitter 2.0.0 with .NET 8. Applications that compile affected generated clients from untrusted OpenAPI descriptions are at risk; administrators should upgrade to Refitter 2.1.2 or later, use trusted descriptions and review generated code before compilation.
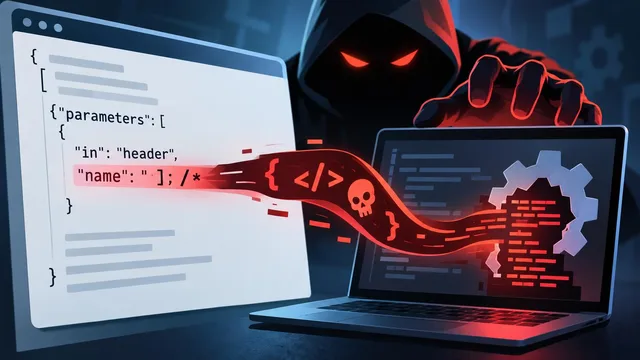 SecurityRefitter advisory warns of code-execution flaw in versions before 2.1.2A security advisory reports that Refitter can generate unsafe code from unescaped header parameter names in OpenAPI descriptions. The issue affects Refitter versions before 2.1.2, and the advisory says it was verified with version 2.0.0 on .NET 8. Applications that compile clients from attacker-controlled or attacker-influenced descriptions may run code when the generated assembly loads; the advisory recommends updating to Refitter 2.1.2 or later and using trusted descriptions.