
Apache Axis flaw could let unauthenticated attackers execute code
- Unsafe reflection vulnerability
- Remote unauthenticated exploitation
- Apache Axis
- Java reflection
- Software security
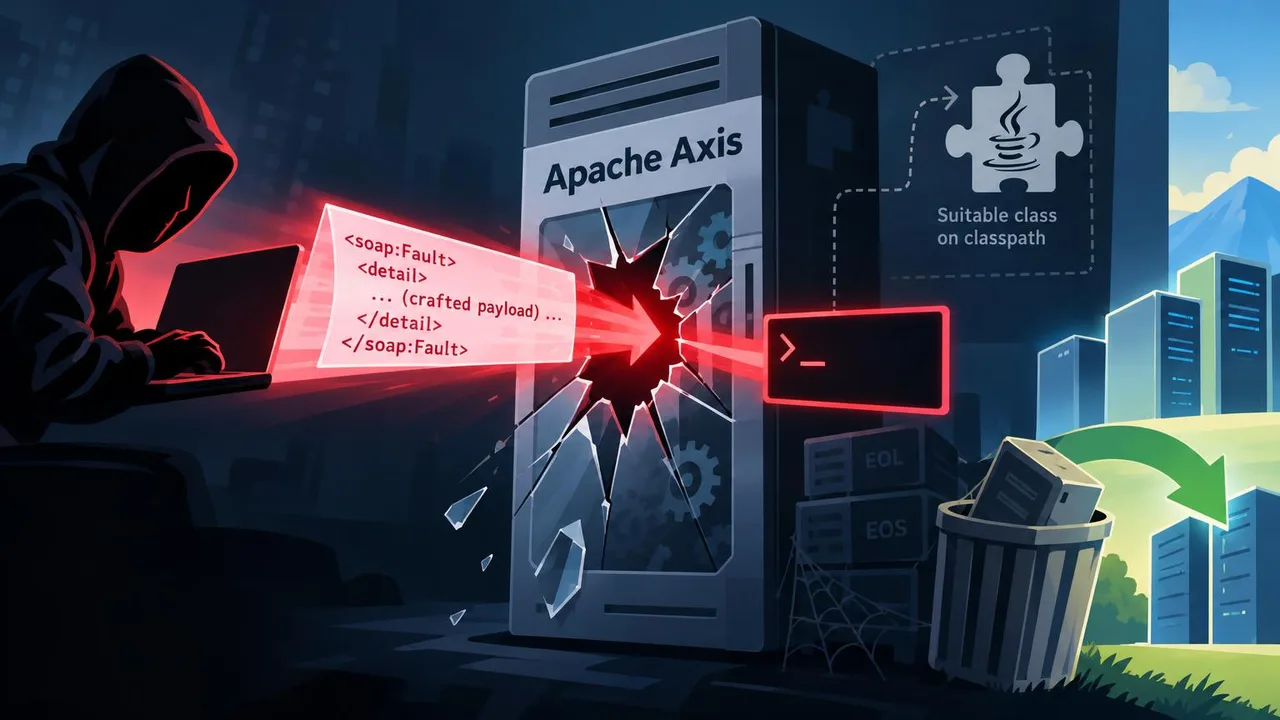
Apache Axis contains an unsafe reflection vulnerability that could let an unauthenticated remote attacker execute arbitrary code through a crafted SOAP fault message. The original advisory does not give an event date.
The vulnerability can cause Axis to load and instantiate a class specified by an attacker, but only when a suitable class is available on the application classpath—the set of code libraries an application can use.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) says affected products may have reached end of life or end of service. It advises users to stop using them or transition to a supported version.
CISA also advises stakeholders to assess each asset’s exposure to the internet and follow BOD 26-04 patching guidance. Where mitigations are unavailable, the advisory says users should discontinue use.



