
GitHub and Microsoft pilot AI-assisted security fixes for six open-source projects
- Codename MDASH
- Open source security
- GitHub
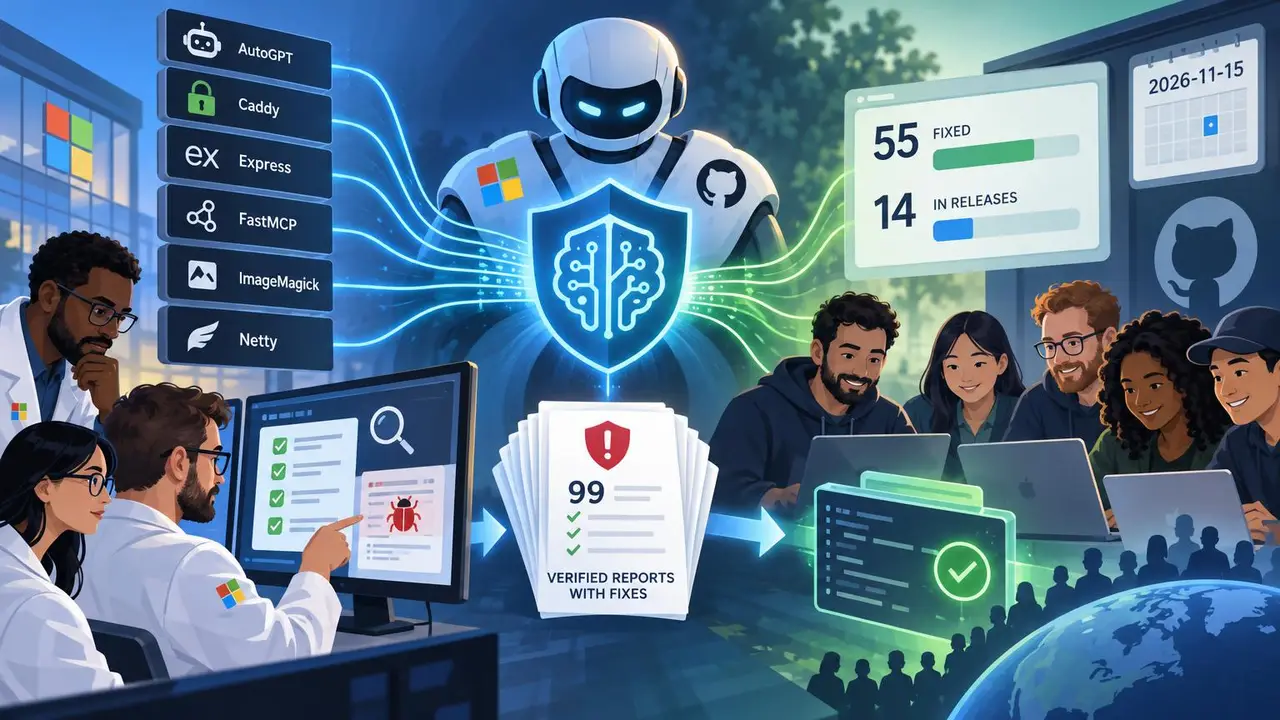
GitHub and Microsoft ran a pilot using Codename MDASH to find and verify security vulnerabilities in six open-source projects, then send maintainers private reports with suggested fixes. The article does not specify when the pilot took place.
Codename MDASH scanned the projects with Microsoft’s MAI Cyber model. GitHub Security Lab used an artificial intelligence triage agent to filter findings, and Microsoft FORGE Lab researchers manually checked every report before it went to maintainers.
The teams sent maintainers 99 private reports, each with a proof of concept and a suggested fix. As of November 15, maintainers had fixed 55 reported vulnerabilities, and 14 fixes were included in a release.
The participating projects were AutoGPT, Caddy, Express, FastMCP, ImageMagick and Netty. Their maintainers agreed to the scans and decided whether and when to make fixes. The pilot was a limited test, not a general release.
Key terms explained
- vulnerability
A vulnerability is a security flaw or weakness in software code that an attacker could exploit. It represents a point in a system where security can be compromised.
Think of it this way. It is like leaving a window unlocked in your house, which an intruder could use to gain entry.



