
Remote code execution vulnerability found in jane-php/open-api-3
- RCE
- PHPDoc
- OpenAPI
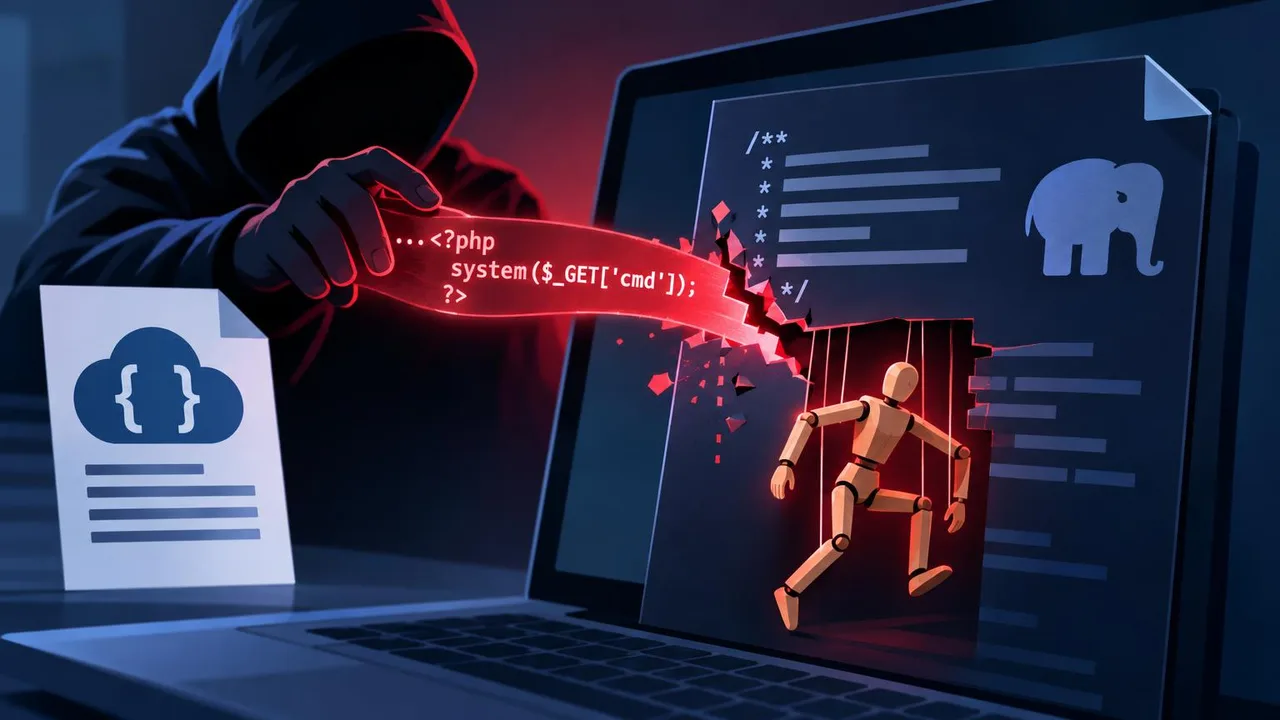
Flaw allows malicious code injection via PHPDoc comments
Update to version 7.12.0 to address the security risk
A security vulnerability in the jane-php/open-api-3 package allows for remote code execution (RCE) by exploiting how the software generates PHP documentation. The issue occurs because the tool emits PHPDoc comment text in a raw format without properly escaping parameter descriptions.
An attacker can exploit this by injecting a */ sequence into a parameter description within an OpenAPI document. This sequence prematurely closes the PHPDoc comment block and allows the attacker to inject arbitrary PHP code directly into the generated client class. When an application instantiates the compromised client, the injected code executes, leading to potential system compromise.
This vulnerability was verified in version 7.11.2 of the package. Developers are advised to update to version 7.12.0, which includes a patch to address this flaw.



