
cassandra-jdbc-wrapper fixes flaw that exposed authentication tokens in logs
- cassandra-jdbc-wrapper
- Token exposure
- Log security
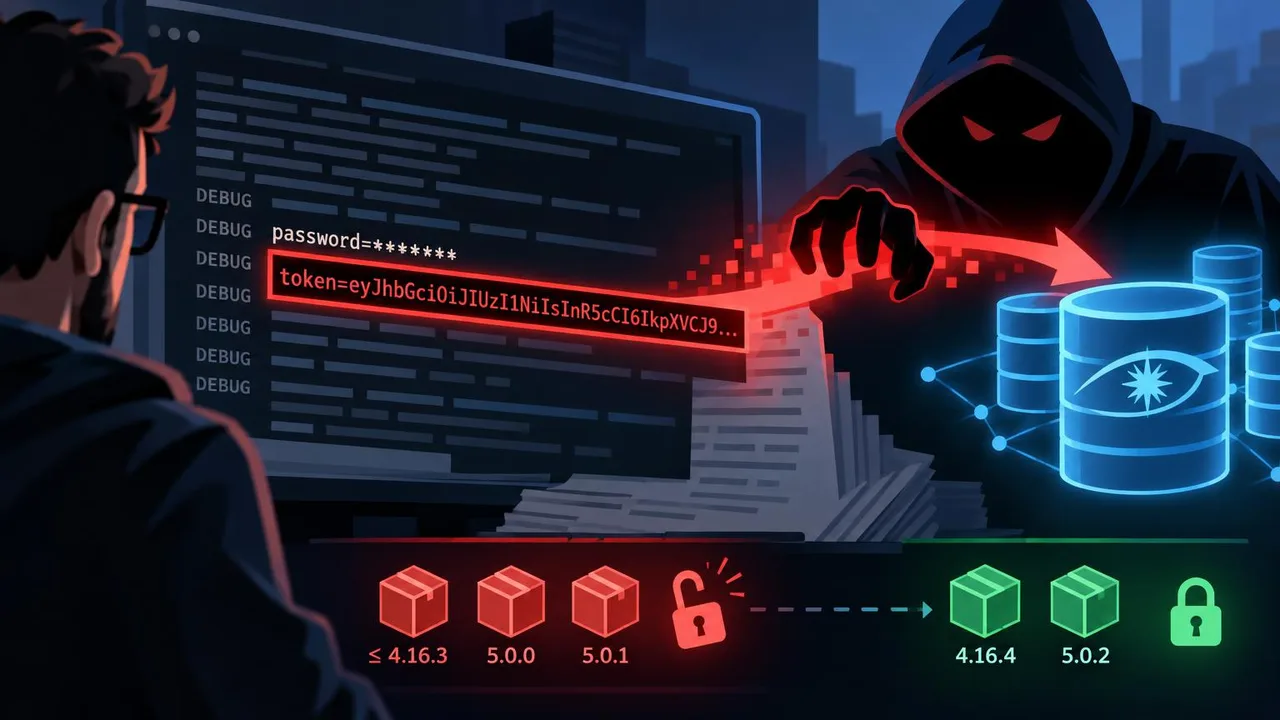
The maintainers of cassandra-jdbc-wrapper fixed a vulnerability that could write authentication tokens in plaintext to application logs. The flaw affects versions 5.0.0 through releases before 5.0.2, and versions up to and including 4.16.3.
The exposure occurs when an application uses token-based Cassandra authentication, including with DataStax Astra, and DEBUG logging is enabled. In those conditions, the library’s two redaction helpers mask passwords but fail to mask the token property. An attacker who can access the logs could use an exposed token to access the Cassandra data it is authorized to read or write.
The advisory classifies the flaw as CWE-532, insertion of sensitive information into a log file. The maintainers fixed it in versions 5.0.2 and 4.16.4. The earlier AIKIDO-2024-10565 fix addressed password logging but did not cover authentication tokens.



