
Chainguard fixes SDK flaw that enabled AWS identity token replay
- Chainguard SDK
- AWS SigV4
- Token replay
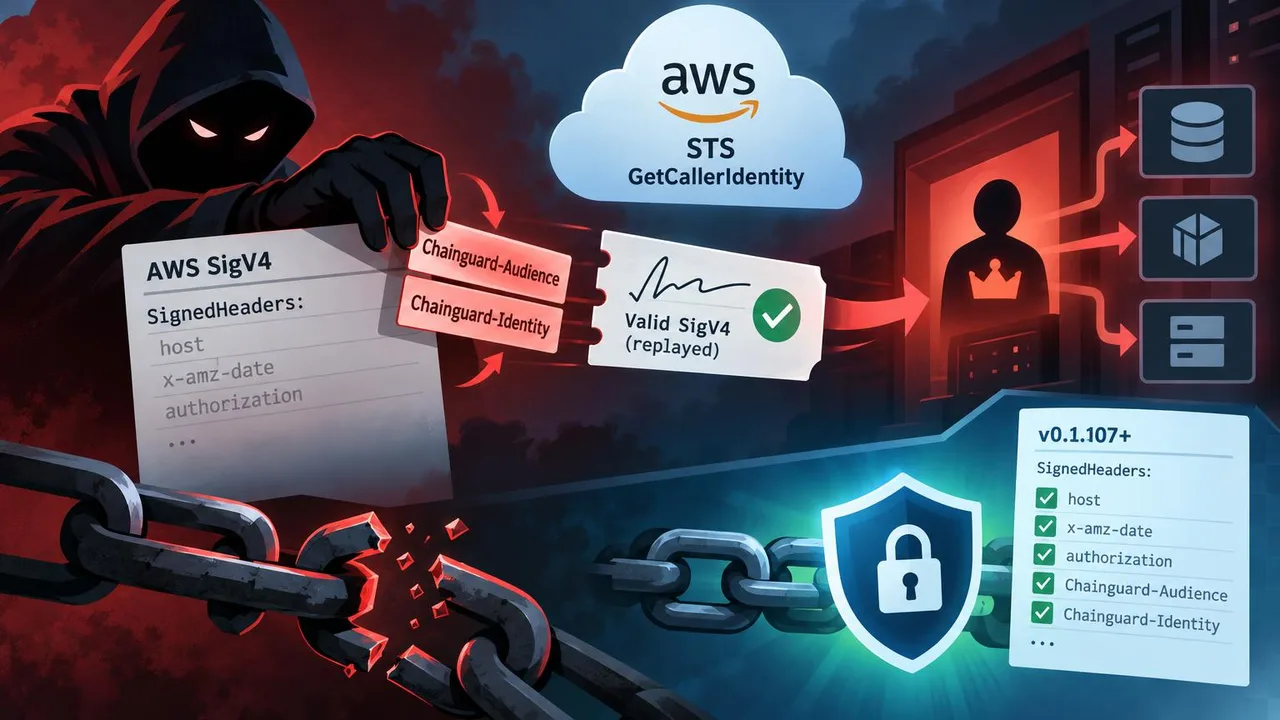
Chainguard said its chainguard.dev/sdk Go library could let attackers replay AWS identity requests against services using its VerifyToken function. The flaw affects versions through v0.1.106 and was fixed in v0.1.107.
The function read the Chainguard-Audience and Chainguard-Identity headers but did not require AWS Signature Version 4 (SigV4) to cover them. Because AWS Security Token Service (STS) checks only headers listed in the signature’s SignedHeaders field, an attacker could alter those headers after a victim signed a GetCallerIdentity request for another service, then replay the still-valid request to a service using VerifyToken.
The replay could make a service accept the request as proof of the victim’s AWS identity for an attacker-chosen audience and identity. The request remains valid for about 15 minutes; an attacker does not need the victim’s AWS credentials, but does need a fresh signed request from the victim’s AWS identity.
Chainguard’s v0.1.107 fix requires both binding headers to appear in SignedHeaders and adds checks for the request method, STS host and timestamp. The issue affects verifiers using VerifyToken; code that only uses the token-generation function GenerateToken is not affected. Chainguard advises operators using VerifyToken to upgrade to v0.1.107 or later.



