
connorbritain patches SQL injection flaw in mssql-mcp packages
- unparameterized WHERE clauses
- identifier allowlist validation
- version 0.6.0 patch
- mssql-mcp-core
- SQL injection
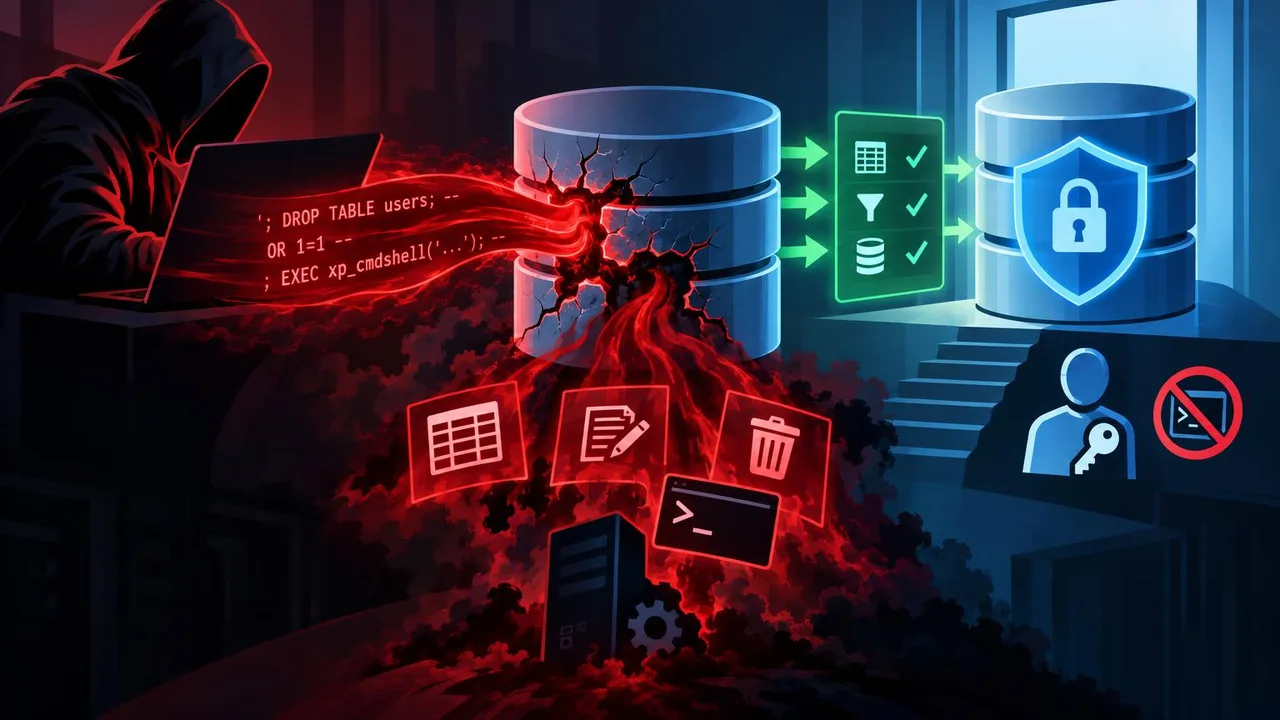
connorbritain patched a SQL injection vulnerability affecting tools in the mssql-mcp package family. The flaw involved unparameterized table names and WHERE clauses, which are used to select and filter database records.
An attacker able to supply tool arguments could read, modify or delete arbitrary data, bypass some validation and safeguards, and potentially execute operating-system commands. The command-execution risk is conditional.
Affected versions are mssql-mcp-core through 0.5.0, mssql-mcp-reader through 0.4.2, mssql-mcp-server through 0.5.2 and mssql-mcp-writer through 0.4.2. The fixes are in versions 0.6.0, 0.5.0, 0.6.0 and 0.5.0, respectively.
The patches validate database identifiers against an allowlist and replace free-form WHERE clauses with structured filters whose values are parameterized. The advisory says upgrading is the only complete fix; it also recommends limiting tool access and using a least-privilege SQL account with xp_cmdshell disabled as additional safeguards.



