
install-artifact-from-github 1.7.0 adds integrity checks for downloaded native artifacts
- CVE-2026-73864
- Artifact integrity
- GitHub artifacts
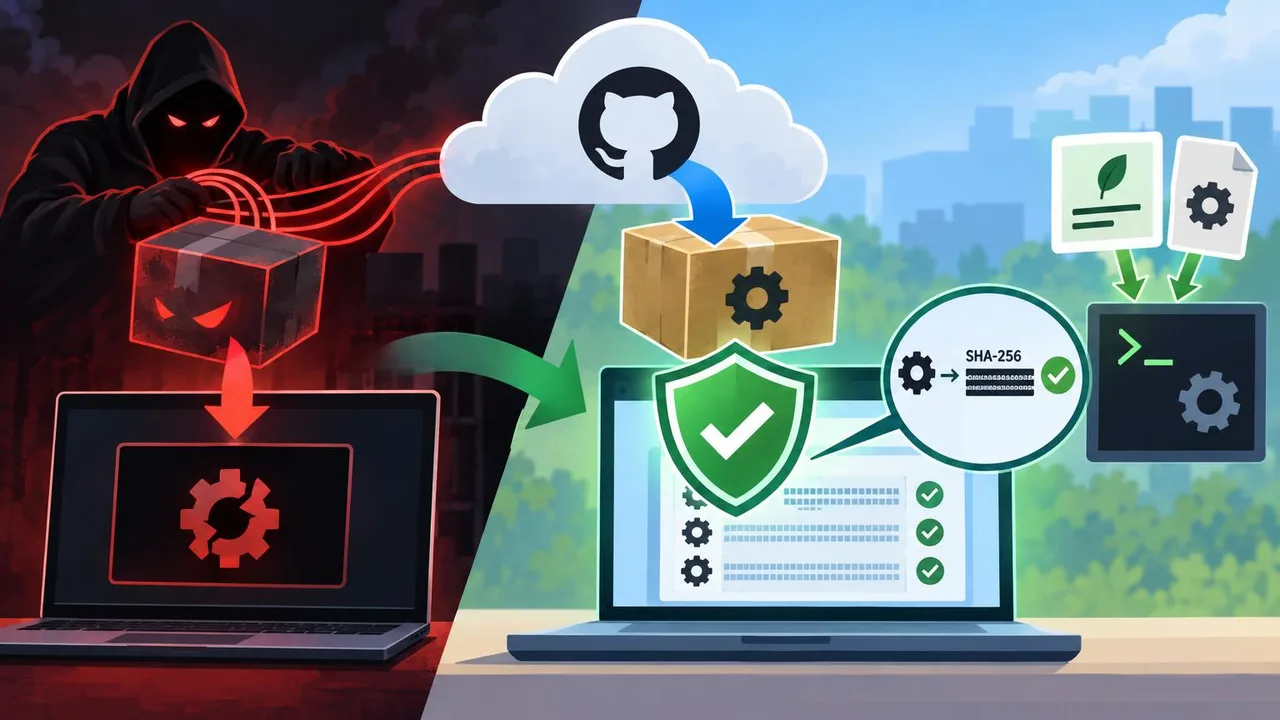
The maintainers of install-artifact-from-github fixed a vulnerability in version 1.7.0 that allowed downloaded native artifacts to be loaded without integrity checks. The flaw affected versions 1.6.0 and earlier, leaving downloads susceptible to interception or transport downgrades.
Version 1.7.0 checks downloaded artifacts against an artifactHashes map containing SHA-256 hashes of decompressed binaries. If a hash does not match or an expected entry is missing, the package rejects the download and falls back to building from source. The verification applies to downloads from the default github.com source, not explicitly configured mirrors.
The check activates only when the consuming package includes an artifactHashes map; packages without one continue to operate as before and do not receive the verification. For affected versions, the advisory describes building from source as a workaround.



