
Flaw in jane-php/open-api-3 enables code execution when generated clients are instantiated
- RCE
- PHPDoc
- OpenAPI
CWE-94
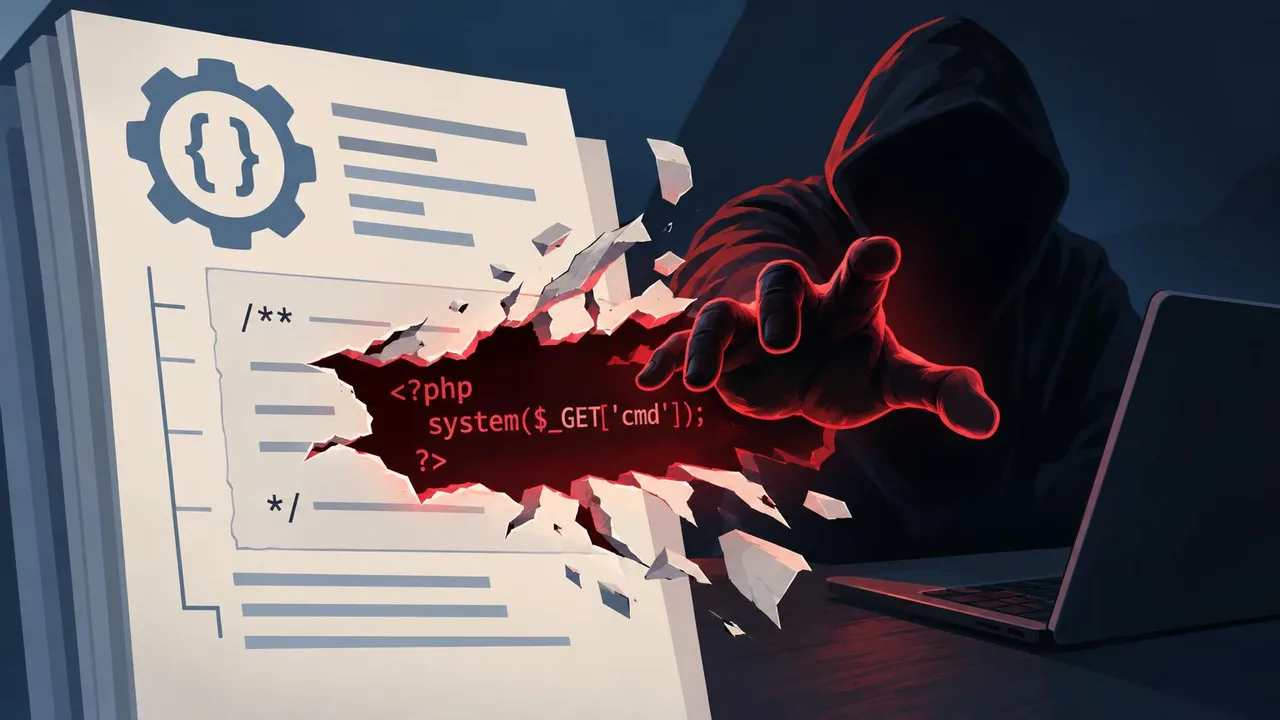
Flaw stems from improper PHPDoc comment escaping
Attackers can inject arbitrary code into generated classes
Update to version 7.12.0 to address the security risk
The jane-php/open-api-3 package has a vulnerability that can lead to remote code execution when an application instantiates a generated client. GitHub Advisories reports that versions earlier than 7.12.0 are affected.
The flaw stems from the package inserting PHPDoc text into generated PHP code without escaping it. PHPDoc is a comment format used to document code and its types; a query parameter name from an attacker-influenced OpenAPI document can break out of a generated comment and inject code into the client class. That code runs when the client is instantiated. The vulnerability is classified as CWE-94, which covers improper control of code generation.
The issue was verified in version 7.11.2 running on PHP 8.1. Version 7.12.0 contains the fix.
Key terms explained
- PHPDoc
PHPDoc is a standard format used to document PHP code elements like classes and methods. It allows developers to describe the purpose and structure of their code directly within the source file.
- CWE-94
CWE-94 refers to a vulnerability where a system fails to properly handle external input used to generate code. This failure allows an attacker to inject unauthorized instructions into the application.
Think of it this way. It is like a chef who lets a customer write their own ingredients on a menu, and the chef accidentally cooks whatever the customer wrote instead of the intended dish.
- OpenAPI
OpenAPI is a standardized way to describe HTTP APIs so that both people and machines can understand how to interact with a service. It provides a clear interface definition without requiring access to the underlying source code.



