
LLMKube flaw could let users read controller or node files
- Model.spec.source input validation
- LLMKube
- Path Traversal
- Version 0.9.0
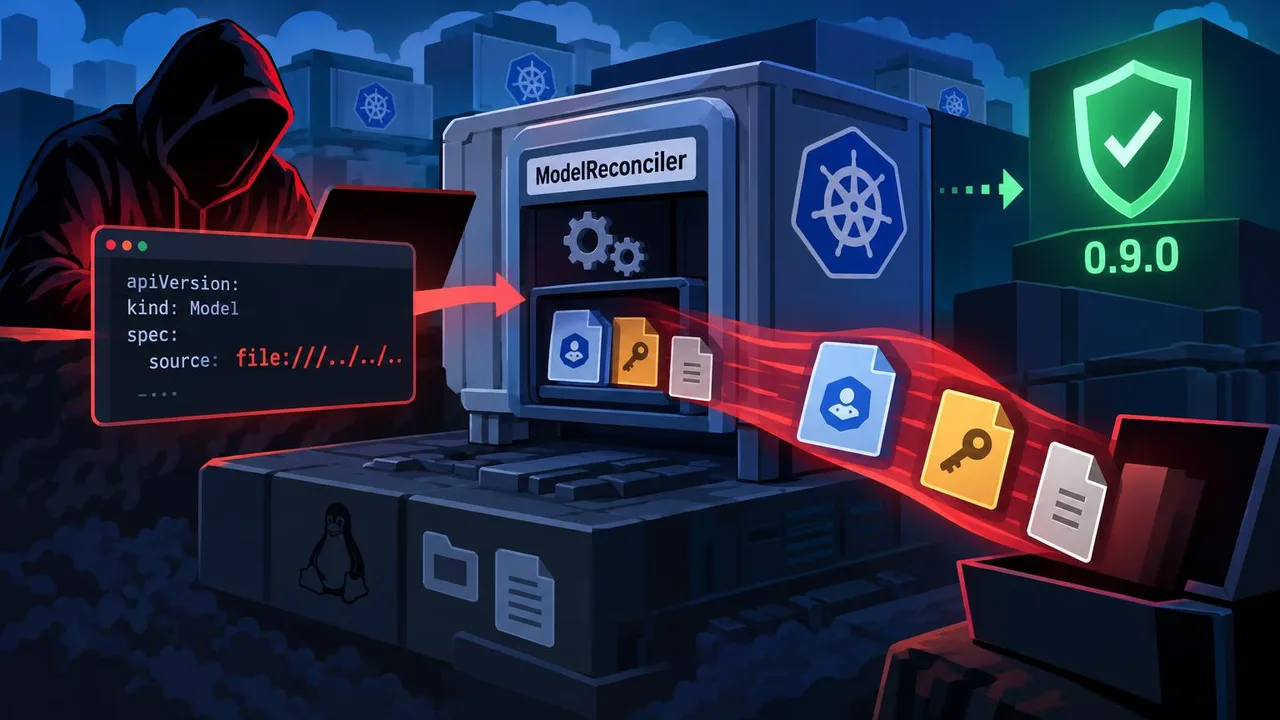
A vulnerability in LLMKube can let a user with permission to write certain namespaced Kubernetes resources read files accessible to the controller pod or the node running an inference pod. GitHub’s advisory classifies the flaw as a path traversal vulnerability, CWE-22.
The flaw affects LLMKube versions 0.8.28 and earlier. The advisory says the software does not restrict paths supplied through the model source field, and that model caching—which enables one of the file-reading paths—is on by default in the CLI and official Helm chart.
The advisory rates the vulnerability 7.7, High, on the CVSS v3.1 scale. LLMKube fixed the issue in version 0.9.0.
Key terms explained
- Path Traversal
Path traversal is a security vulnerability that allows unauthorized access to files and directories outside of an intended restricted folder. It occurs when an application fails to properly validate user input used to construct file paths.
Think of it this way. This is like a guest in a hotel who uses a master key to enter rooms they did not book, instead of staying only in their assigned room.
- CWE-22
CWE-22 refers to the improper limitation of a pathname to a restricted directory. It occurs when an application fails to neutralize special characters in user input, allowing access to files outside the intended scope.
Think of it this way. This is like a librarian who accepts a request for a book but fails to check if the user is trying to sneak into the restricted archives.



