
CVE.org designates Symfony as a CVE Numbering Authority
- Symfony
- CVE Numbering Authority
- Twig
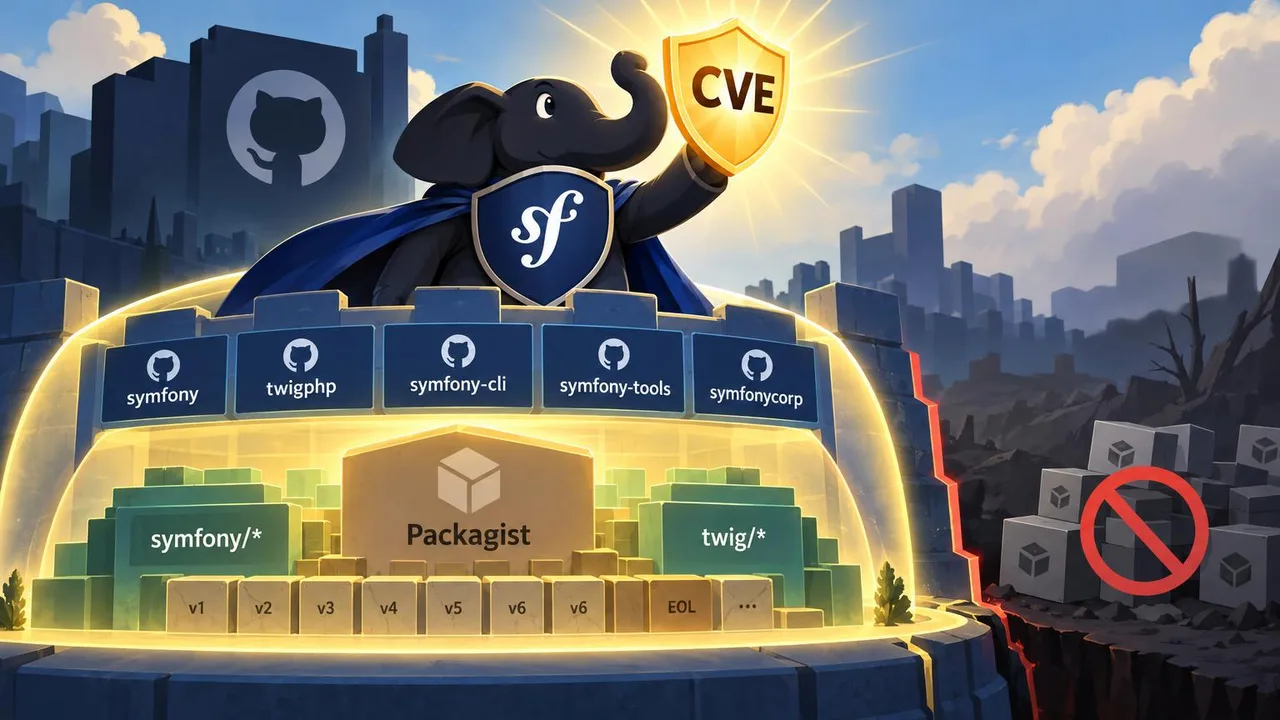
CVE.org designated Symfony as a CVE Numbering Authority (CNA) for software published by the Symfony project. A CNA can assign CVE identifiers to report vulnerabilities in the software within its authorized scope.
The authorization covers software in the symfony, twigphp, symfony-cli, symfony-tools and symfonycorp GitHub organizations. It also includes corresponding packages distributed through Packagist under the symfony and twig vendor namespaces.
The scope includes every version of the covered software, including end-of-life branches. Third-party packages that depend on Symfony or Twig, such as community bundles, are excluded.



