
Kubernetes SIG Network plans to remove kube-proxy IPVS backend in 1.40
- Maintenance complexity issues
- Kubernetes
kube-proxy- ipvs
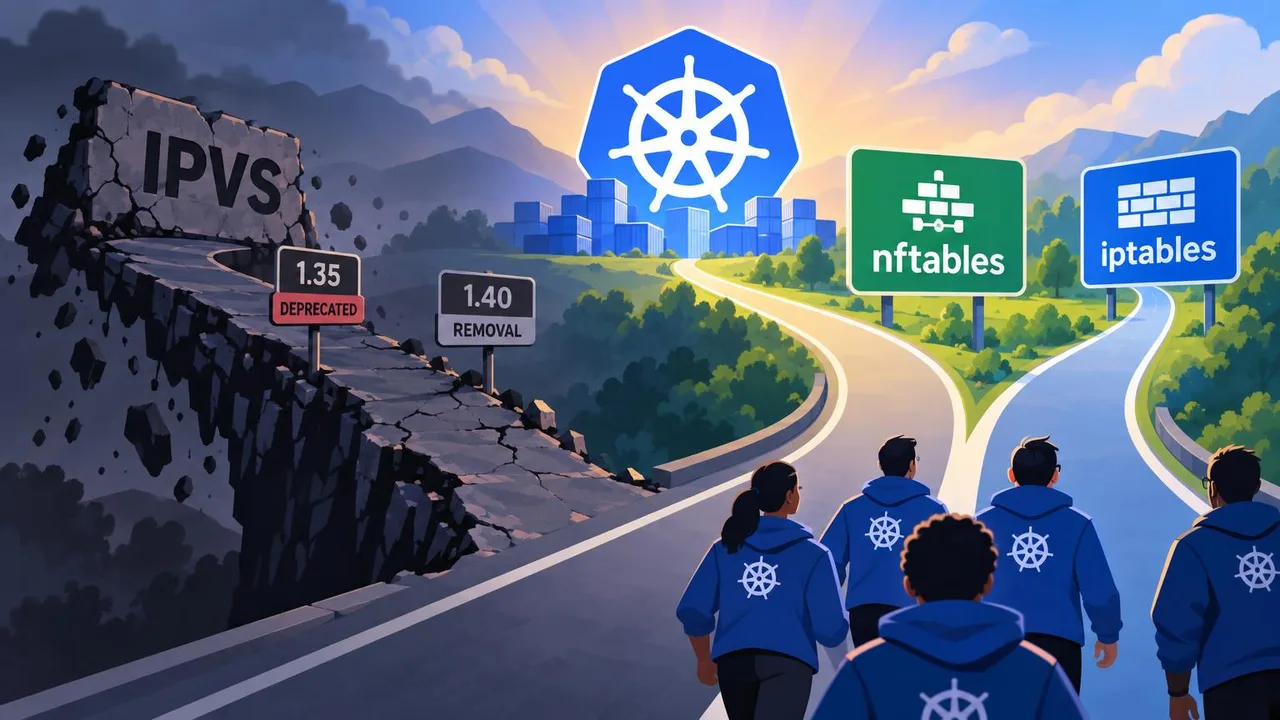
Kubernetes SIG Network deprecated the IPVS backend for kube-proxy in Kubernetes 1.35 and plans to remove it in Kubernetes 1.40. The backend remains available with a deprecation warning, but users should plan to switch to nftables or iptables.
The IPVS backend was designed to improve two kinds of performance problems in iptables. Data-plane latency is the time clients take to establish connections to services; control-plane latency is how quickly kube-proxy processes service and endpoint changes and updates its rules. IPVS addressed both, but its kernel interface does not support every Kubernetes Service feature, and the backend is complex to maintain and differs architecturally from the other backends.
Kubernetes introduced the nftables backend in version 1.29, and it became generally available in version 1.33. The project intended it eventually to replace both IPVS and iptables. Kubernetes SIG Network recommends that IPVS users plan a migration to either backend ahead of the planned removal in version 1.40.
Key terms explained
- kube-proxy
Kube-proxy is a network component that runs on each node to manage service communication by forwarding traffic to the appropriate backends.



