
djangocms-versioning fixes authorization bypass affecting versions through 2.6.0
- CVE-2026-69138
- djangocms-versioning
- Authorization bypass
- Security patch
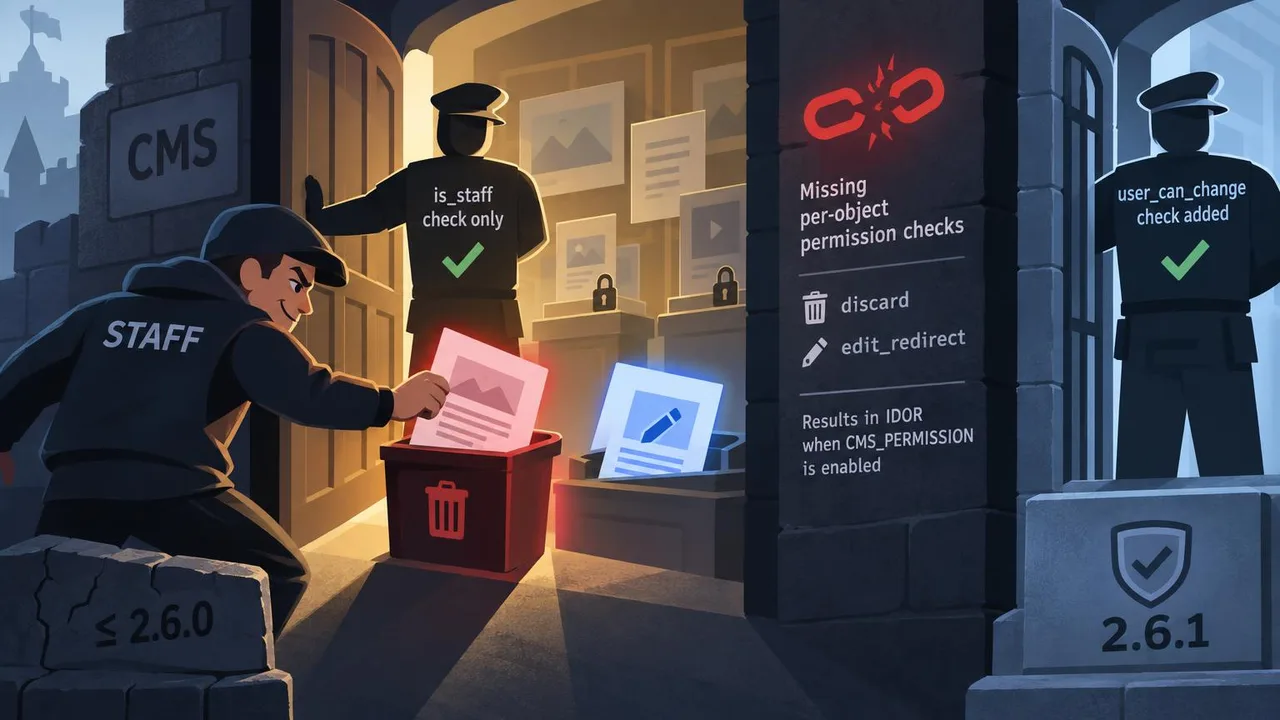
The djangocms-versioning maintainers fixed an authorization bypass in the package, affecting versions through 2.6.0. The flaw let staff users carry out version changes on content they were not authorized to modify.
The affected discard transition could delete a draft version and its underlying content object. The edit_redirect transition could create an editable draft from published content. Both lacked a check that the user had permission to change that specific object, allowing the flaw to be exploited by supplying a version’s primary key.
With CMS_PERMISSION = True, the affected operations effectively relied only on whether a user was staff. The maintainers fixed the issue by adding a user_can_change check to both transitions. They recommend upgrading to djangocms-versioning 2.6.1 or later.
Key terms explained
- authorization bypass
An authorization bypass occurs when a system fails to properly verify if a user has the necessary permissions to access or modify specific data. This often happens when the system relies on user-provided identifiers that can be manipulated to access unauthorized records.
Think of it this way. It is like someone using a master key to open any door in a building because the locks were never checked to see if the person actually had permission to enter those specific rooms.
- djangocms-versioning
djangocms-versioning is a software package that provides version control features for content managed within the django CMS platform. It allows editors to manage content states such as drafts and published versions.



