
Contao flaw lets page editors store scripts in search results
- Contao
- frontend search
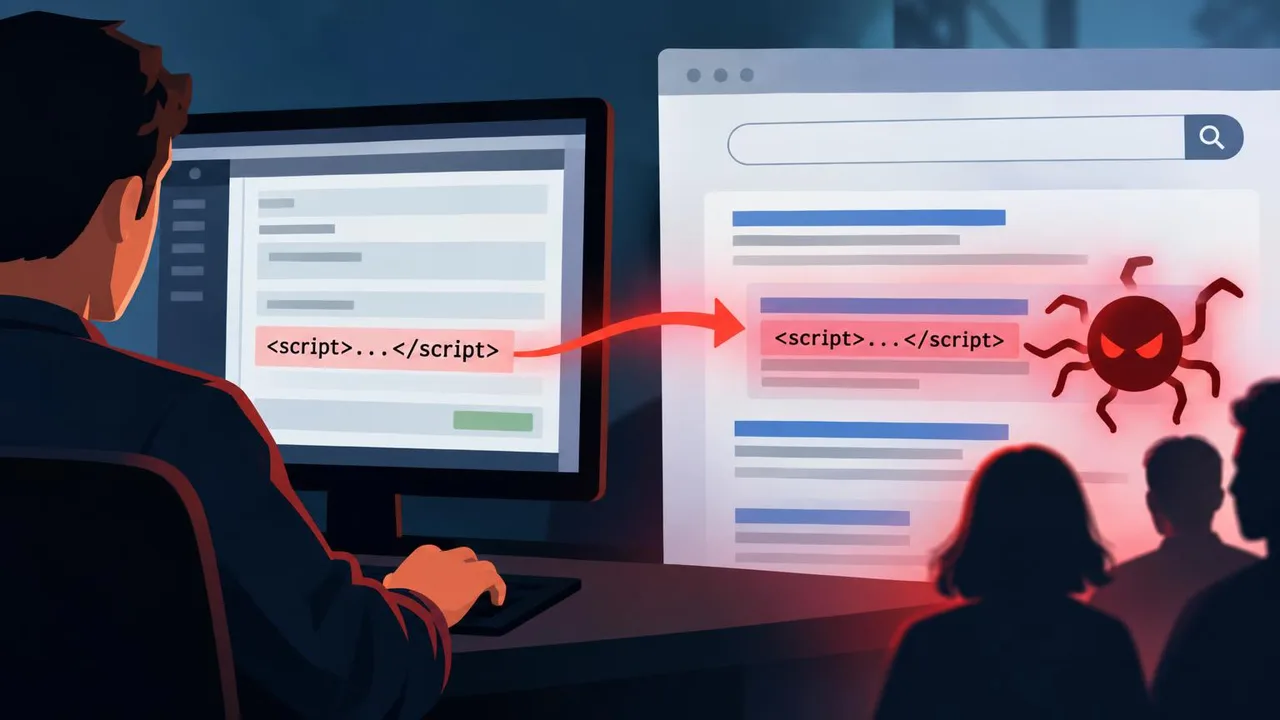
The risk requires the legacy search template to be active
Default Twig installations are not affected
A backend page editor can store a script that runs in Contao’s frontend search results when the search module uses the legacy template. GitHub published the advisory on November 20, 2026.
The flaw is in the legacy search_default.html5 template, which outputs the link variable without escaping it. The stored script can run in the browsers of anonymous visitors and administrators who view search results.
The vulnerability applies only when the legacy template is active for the search module. Default Twig installations using search_default.html.twig are not affected because Twig automatically escapes output.



