
django-filer fixes folder-permission flaw in version 3.5.0
- Unauthorized file deletion
- FILER_ENABLE_PERMISSIONS flaw
- CVE-2026-69131
- django-filer
- File deletion
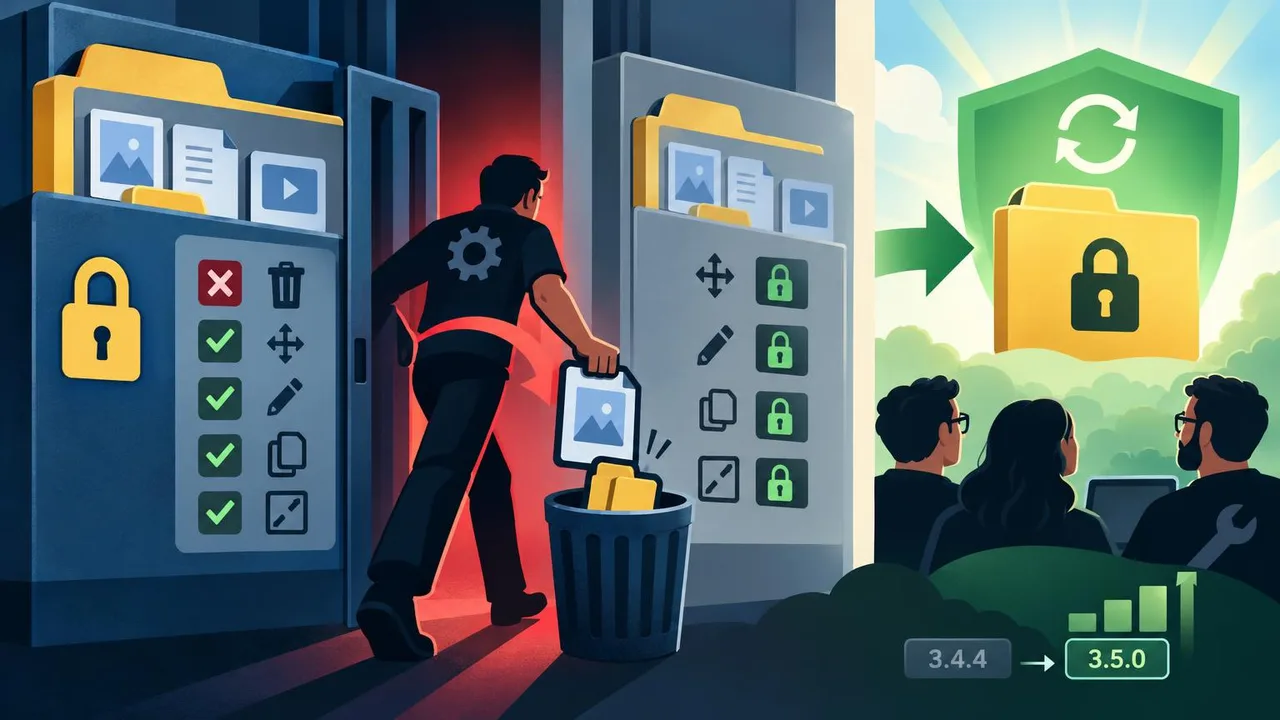
django-filer maintainers fixed a vulnerability in the package’s file-and-folder deletion admin action in version 3.5.0. The flaw could let some staff delete files and subfolders in folders where they had read-only access.
The issue affected installations with the optional per-folder permission system enabled using FILER_ENABLE_PERMISSIONS=True. Staff users with global Django model-level delete permissions could bypass folder-level restrictions; the flaw concerned deletion controls, not access to confidential files.
The vulnerability affected django-filer versions up to and including 3.4.4. Installations using the default setting, with per-folder permissions disabled, were not affected by this specific issue. The maintainers fixed it in version 3.5.0; until upgrading, the advisory recommends not granting global delete permissions to staff who should have read-only access to particular folders.



