
Vanderbilt REDCap flaw could allow unauthenticated code execution
- REDCap
- Code injection
- Application security
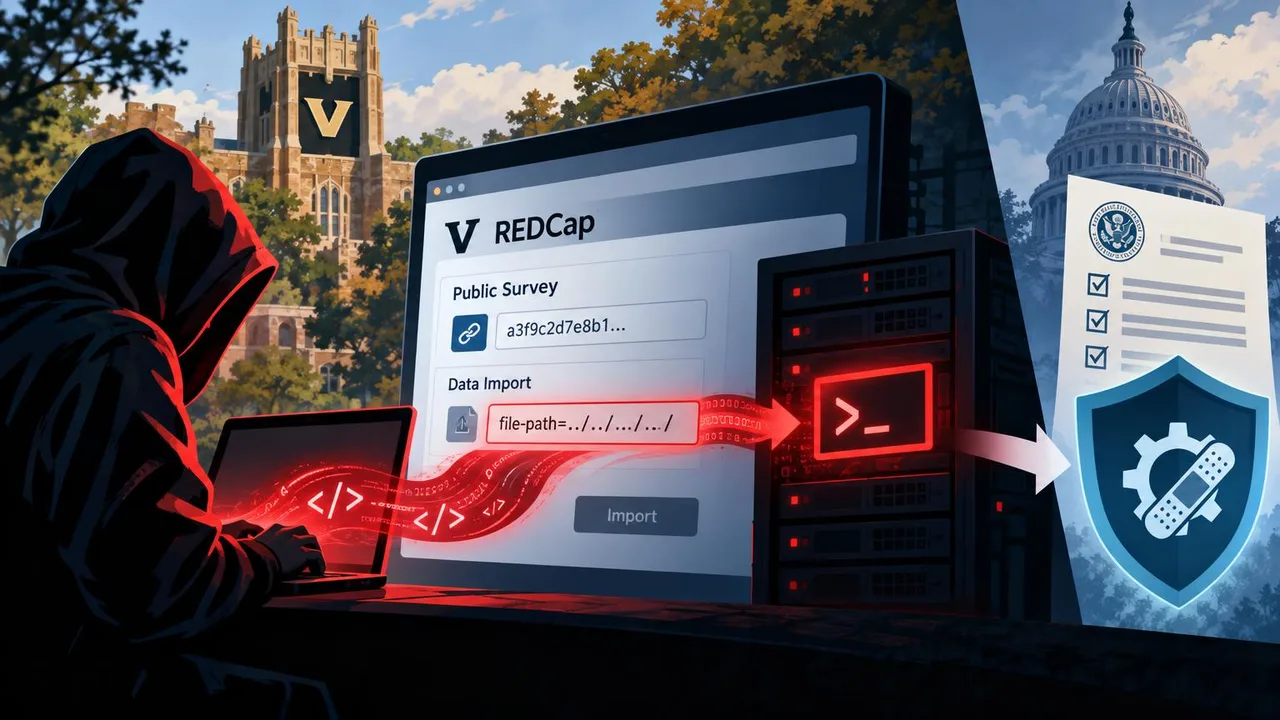
Vanderbilt University’s Research Electronic Data Capture (REDCap) contains a code injection vulnerability that could allow an unauthenticated attacker to execute arbitrary code on a server. The advisory does not identify an event date or affected versions.
An attacker could exploit the flaw by sending HTTP requests that reach an unintended controller route from a public survey context and providing a crafted file-path or stream parameter during data-import processing. Exploitation requires knowledge of a valid public survey hash.
The advisory recommends applying mitigations according to vendor instructions and following applicable Cybersecurity and Infrastructure Security Agency (CISA) guidance on prioritizing security updates and forensic triage. Stakeholders should assess each asset’s internet exposure and follow applicable patching guidance. If mitigations are unavailable, the advisory says to follow applicable guidance for cloud services or discontinue use of the product.



